Bitsler provably fair games
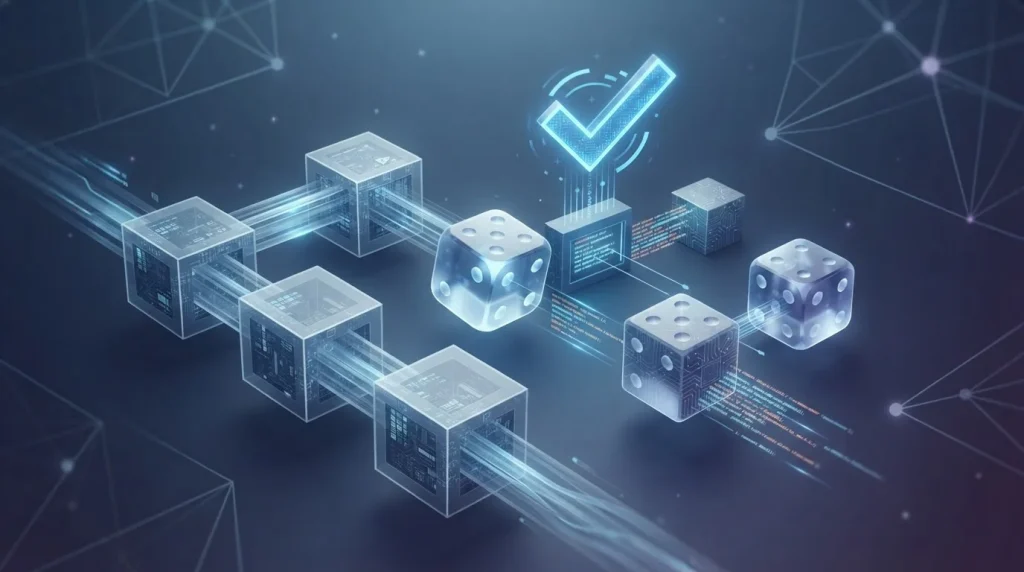
Table of Contents
- Provably fair belongs to the Bitsler Originals side
- A hash-and-seed check follows a simple logic
- Verification can prove integrity without proving value
- A practical check should be repeatable rather than ceremonial
- Fairness checks do not remove variance or bankroll risk
- The feature fits Bitsler's Bitcoin-dice heritage
- Common questions about Bitsler provably fair games
- Use provably fair as an audit trail, not a betting signal
Section element
Outcome verification
Bitsler Originals include provably fair games with cryptographic hash verification. The useful part is not the label itself: it is the ability to check whether a completed result matches the cryptographic inputs committed to the round. That check is meaningful, but it answers a narrow question and should not be confused with judging whether a wager was sensible or profitable.
Provably fair belongs to the Bitsler Originals side
Bitsler’s in-house Originals include provably fair verification. That makes the feature most relevant when you are playing the casino’s own software games rather than treating it as a blanket description for every title in the wider game lobby.
- ScopeBitsler Originals
- VerificationCryptographic hash check
- HeritageBitcoin dice
- Established2015
The Bitsler Originals guide maps the in-house catalog, including Dice, Ultimate Dice, Crash Pro, Mines, Plinko, Roulette, Keno, Blackjack, Video Poker and other titles. Provably fair is the technical layer that matters when you want to inspect the integrity of a completed result on that side of the casino.
The game still has its own rules
A verification layer does not replace the paytable, probability model or round mechanics. Read the individual game information before deciding what an outcome means for your bankroll.
The proof belongs to the result
The useful question is whether the result can be reproduced from committed cryptographic inputs, not whether the result happened to favor the player.
Third-party games are a separate category
Bitsler also carries thousands of games from outside studios. The broader games guide separates provider content, live dealer tables and in-house Originals rather than treating them as one technical system.
A hash-and-seed check follows a simple logic
Provably fair systems vary in interface, but the core cryptographic idea is straightforward. A game commits to data before the result is fully revealed, then exposes enough information after the round for the player to check whether the final outcome matches that commitment.
- A hidden input is committed cryptographically. In a typical design, the operator creates a server-side seed and publishes a cryptographic hash of it before the relevant round. A hash acts like a one-way fingerprint: it can be checked later without revealing the original seed in advance.
- Player-side or round-specific data is combined with it. Many provably fair systems also use a client seed and a round counter or nonce. These values help make each round distinct. This is a general explanation of the method, not a claim that every Bitsler Original exposes the same fields in the same layout.
- The game produces the outcome from the inputs. A deterministic calculation turns those values into the game result. The important property is repeatability: the same disclosed inputs should reproduce the same output.
- The hidden value is later revealed. Once the relevant seed is disclosed, its hash can be compared with the commitment shown earlier.
- The player repeats the calculation or uses the verifier. If the disclosed values recreate the result and the revealed seed matches its earlier hash, the cryptographic chain is internally consistent.
Verification can prove integrity without proving value
A successful provably fair check is strong evidence about one specific part of the game: whether the disclosed inputs and the recorded outcome fit together. It is not a universal certificate for every question a player might have.
| Question | What a provably fair check can tell you | What still needs separate judgment |
|---|---|---|
| Was the disclosed result consistent with the cryptographic inputs? | A valid recomputation can show that the disclosed inputs reproduce the same result. | You still need to understand the game’s payout rules. |
| Could the committed server value have been swapped after the result? | A matching pre-commitment hash makes an unnoticed post-result change detectable. | You still need to know when and how the commitment was presented. |
| Was the wager likely to win? | No. Verification does not turn a random outcome into a prediction. | Probability, house edge and variance remain separate issues. |
| Should you increase the next stake? | No. A valid past result does not create a betting signal for the next round. | Bankroll limits and session discipline remain your responsibility. |
| Is every game in the casino covered by the same verifier? | No such blanket conclusion follows from the presence of provably fair Originals. | Check the verification feature on the specific in-house game you are using. |
This distinction matters because a fair random process can still produce long losing runs. Fairness concerns the integrity of how outcomes are generated and committed; profitability concerns the statistical structure of the game and the stakes you choose.
A practical check should be repeatable rather than ceremonial
Opening a verifier once is less useful than understanding what you are looking for. A good routine is short enough to repeat and clear enough that a mismatch would be obvious.
What to record before or during play
- The commitment or hash presented for the relevant round or seed cycle.
- Any client-side value the game lets you control or inspect.
- The round identifier or nonce where the interface exposes one.
- The actual outcome you intend to verify.
What not to infer from a valid check
- That the next round is more likely to win.
- That a losing streak is due to reverse.
- That higher stakes become safer after several checks pass.
- That every third-party game uses the same cryptographic method.
- Commitment
- A cryptographic fingerprint published before the underlying value is disclosed.
- Seed
- An input used by the deterministic result calculation; designs often combine operator and player-side values.
- Nonce
- A changing round counter used in many systems to distinguish one result from the next.
- Verifier
- A way to recompute the result from the disclosed inputs and compare it with the recorded outcome.
If you want to see where these checks sit among the in-house titles themselves, return to the Originals catalog rather than assuming every game family exposes identical controls.
Fairness checks do not remove variance or bankroll risk
Cryptographic transparency can answer an integrity question while leaving the financial risk of gambling unchanged. A fair game can still have a house edge, large swings and sequences that feel unusual simply because random outcomes cluster.
- Treat every stake as money that can be lost, even when the previous round passes its hash check.
- Set a session loss limit before starting rather than trying to recover a bad sequence.
- Separate technical verification from betting strategy; a hash check is not a forecasting tool.
- Use deposit limits or self-exclusion when gambling stops fitting the limits you set for yourself.
The feature fits Bitsler’s Bitcoin-dice heritage
Bitsler started as a Bitcoin-dice site in 2015 and later expanded into a much larger casino with an in-house Originals catalog. Provably fair verification therefore fits the platform’s original crypto-native identity particularly well: dice and other compact mathematical games are natural places to expose the inputs behind a result.
That heritage does not make every modern title equivalent to the original dice product. The useful continuity is narrower: Bitsler still maintains an in-house game line where cryptographic outcome checking is part of the experience. If you prefer streamed dealer tables instead, the Bitsler live casino guide covers that separate game mode.
Common questions about Bitsler provably fair games
Does Bitsler have provably fair games?
Yes. Bitsler Originals include provably fair games with cryptographic hash verification.
What does provably fair verification actually check?
It checks whether the disclosed cryptographic inputs reproduce the recorded result and whether a revealed value matches the commitment made before disclosure.
Does a valid provably fair result mean the next bet is more likely to win?
No. Verification concerns the integrity of a completed result. It does not predict the next outcome or change the game’s underlying probabilities.
Are all Bitsler games provably fair?
Provably fair verification applies to Bitsler Originals. The wider casino also includes third-party and live-dealer games, so do not assume one verification method covers the entire lobby.
Why is a hash useful in a provably fair system?
A cryptographic hash acts as a fingerprint of a hidden value. When that value is revealed later, the player can hash it again and check whether it matches the earlier commitment.
Use provably fair as an audit trail, not a betting signal
Bitsler’s provably fair Originals add a useful technical property to the in-house catalog: completed outcomes can be tied to cryptographic hash verification rather than accepted as an unexplained black box.
The strongest way to use that feature is narrow and practical. Learn the commitment-and-disclosure flow, repeat a check on completed rounds, and treat a matching result as evidence about integrity only. Game rules, house edge, variance and bankroll exposure remain separate questions no matter how cleanly a hash check passes.